
OpenStack
Overview
Storware Backup & Recovery protects virtual machines running in OpenStack. It discovers instances and their attached volumes, creates backups, and allows you to restore protected data when needed. You can configure backup policies for selected instances and manage protection from the Storware Backup & Recovery interface.
Supported versions
Supported versions
2023.1 Antelope, 2024.1 Caracal, 2025.1 Epoxy, 2025.2 Flamingo, 2026.1 Gazpacho Red Hat OpenStack Platform: 17.1, 18.0 Canonical OpenStack: 2024.1 LTS (Sunbeam), 2024.1 (Charmed) WindRiver Openstack 25.09, WindRiver Cloud Platform 26.03
2023.1 Antelope, 2024.1 Caracal, 2025.1 Epoxy, 2025.2 Flamingo, 2026.1 Gazpacho Red Hat OpenStack Platform: 17.1, 18.0 Canonical OpenStack: 2024.1 LTS (Sunbeam), 2024.1 (Charmed) WindRiver Openstack 25.09, WindRiver Cloud Platform 26.03
The last snapshot is kept on the hypervisor for incremental backups
Yes
No
Access to hypervisor OS required
No
No
Proxy VM required
Yes
Yes
Full backup
Supported
Supported
Incremental backup
Not supported
Supported
Synthetic backups
Supported
Supported
Secondary backup destination
Not supported
Supported
File-level restore
Supported
Supported
VM disk exclusion
Supported
Supported
Quiesced snapshots
Not supported
Not supported
Snapshots management
Supported (Without snapshot revert)
Supported (Without snapshot revert)
Pre/post command execution
Supported
Supported
Access to VM disk backup over iSCSI
Supported
Supported
VM name-based policy assignment
Supported
Supported
VM tag-based policy assignment
Supported
Supported
Power-on VM after restore
Not supported (always on)
Not supported (always on)
Network requirements
Disk attachment with generic incremental
Connection URL: https://KEYSTONE_HOST:5000/v3
Node
Keystone, Nova, Glance, Cinder, Neutron
ports that were defined in endpoints for OpenStack services
API access to the OpenStack management services - using endpoint type that has been specified in hypervisor manager details
Disk attachment to proxy VM (full)
Connection URL: https://KEYSTONE_HOST:5000/v3
Node
Keystone, Nova, Glance, Cinder, Neutron
ports that were defined in endpoints for OpenStack services
API access to the OpenStack management services - using endpoint type that has been specified in hypervisor manager details
Node
Ceph monitors
3300/tcp, 6789/tcp
if Ceph RBD is used as the backend storage - used to collect changed-blocks lists from Ceph
Backup Strategies
Disk Attachment with generic incremental
Automatically selects the incremental method for each volume. It uses native changed-block tracking for Ceph and Pure Storage, and checksum-based processing for other storage backends.
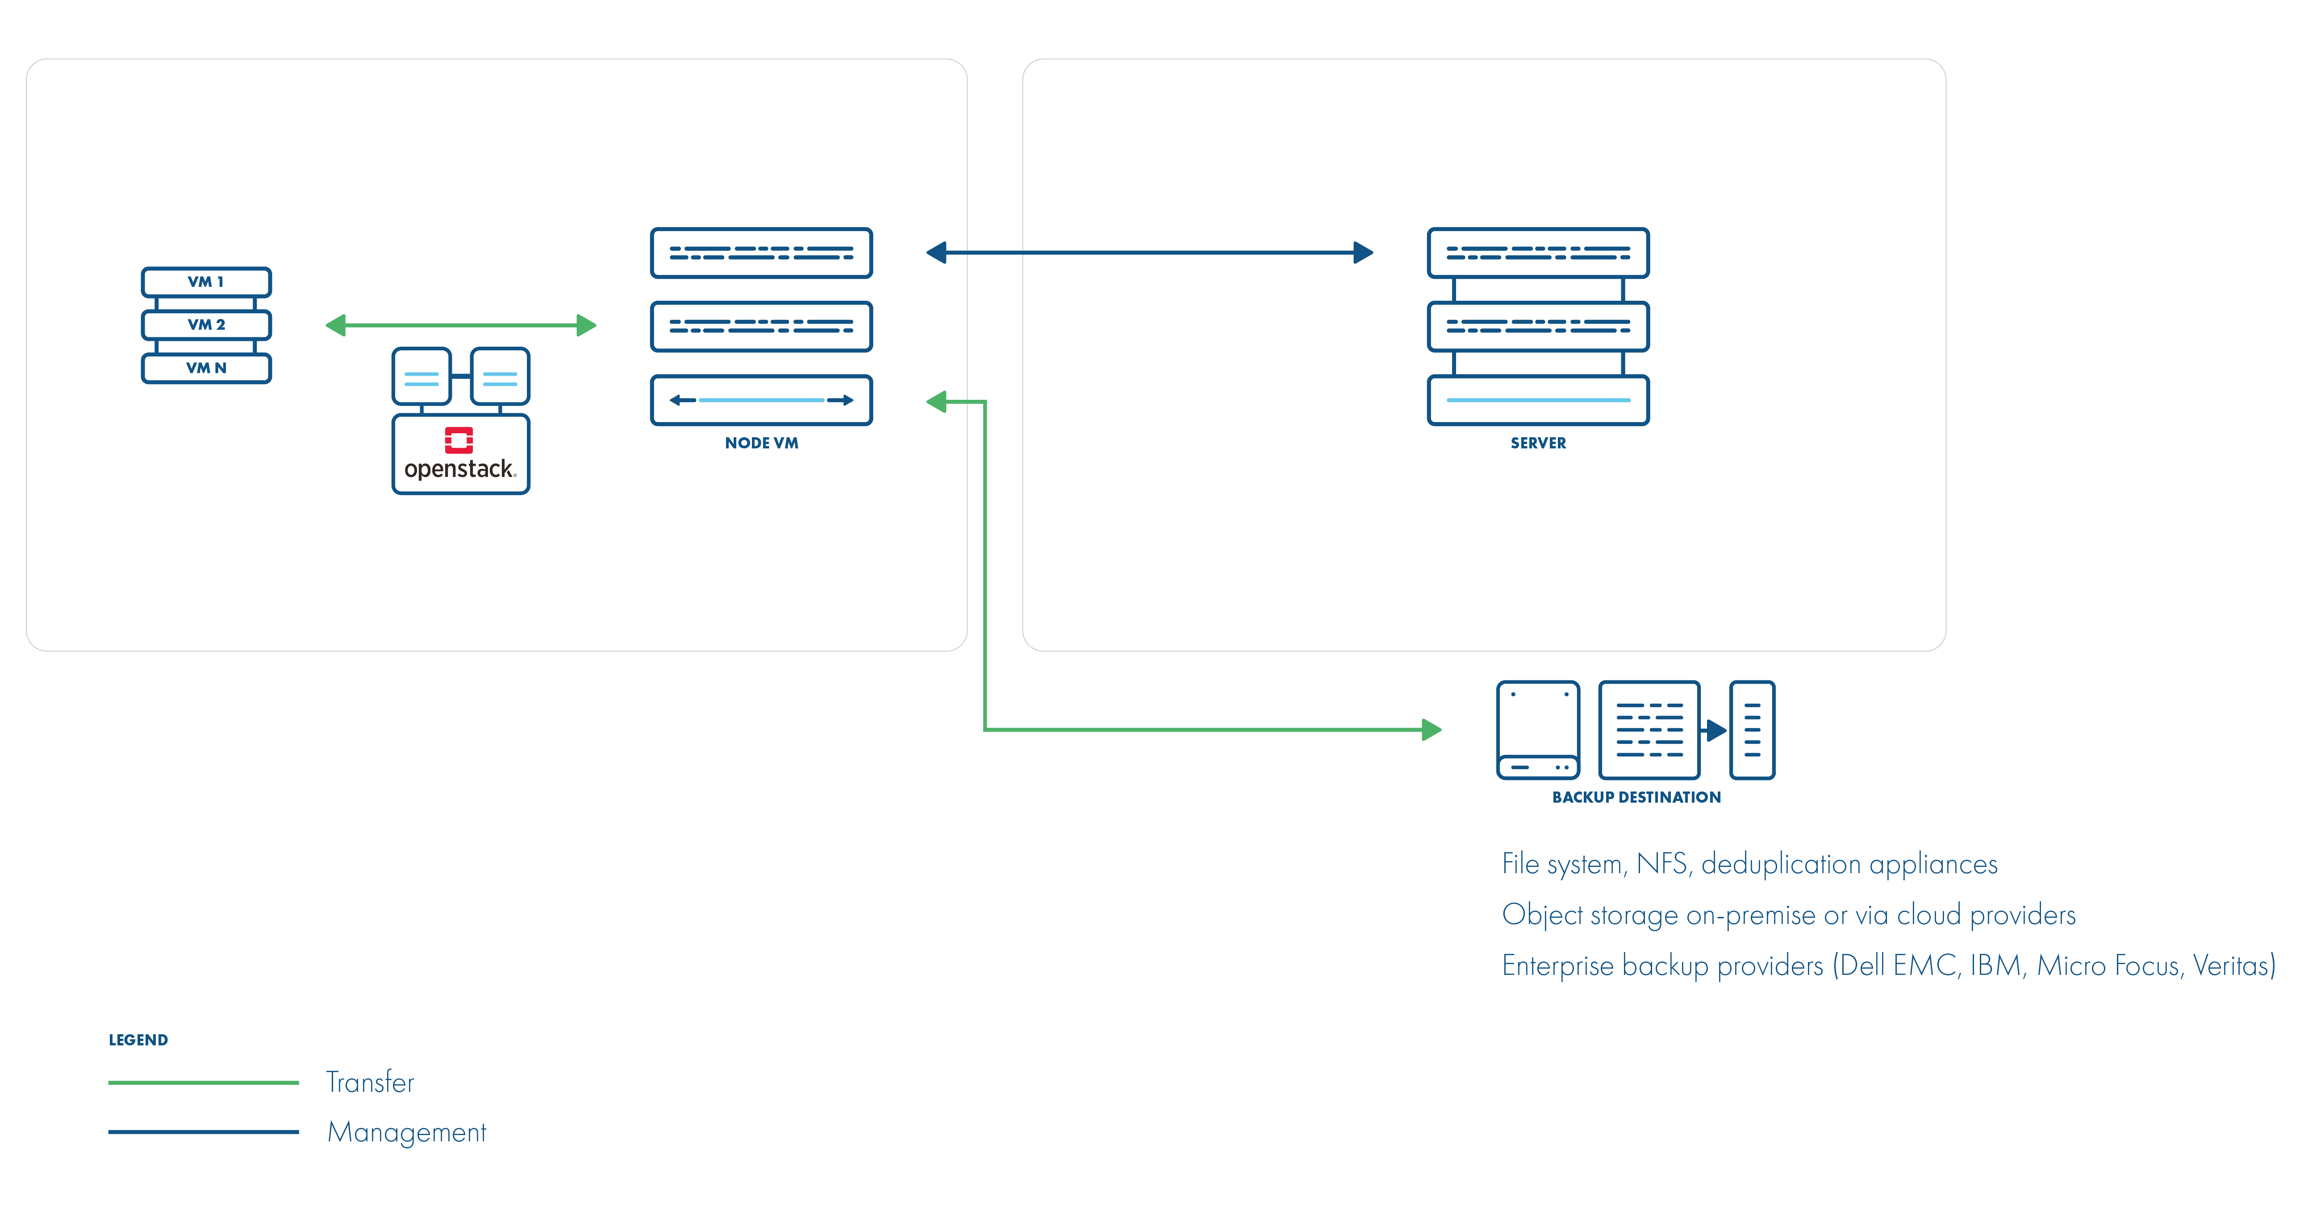
Disk attachment to proxy VM (full) - deprecated
This strategy uses the Cinder API to attach volumes to a proxy VM running Storware Backup & Recovery Node. It supports full backups for Cinder-compatible storage. Incremental backups are available for Ceph RBD volumes when a storage provider is specified in the volume type on the Storage tab.
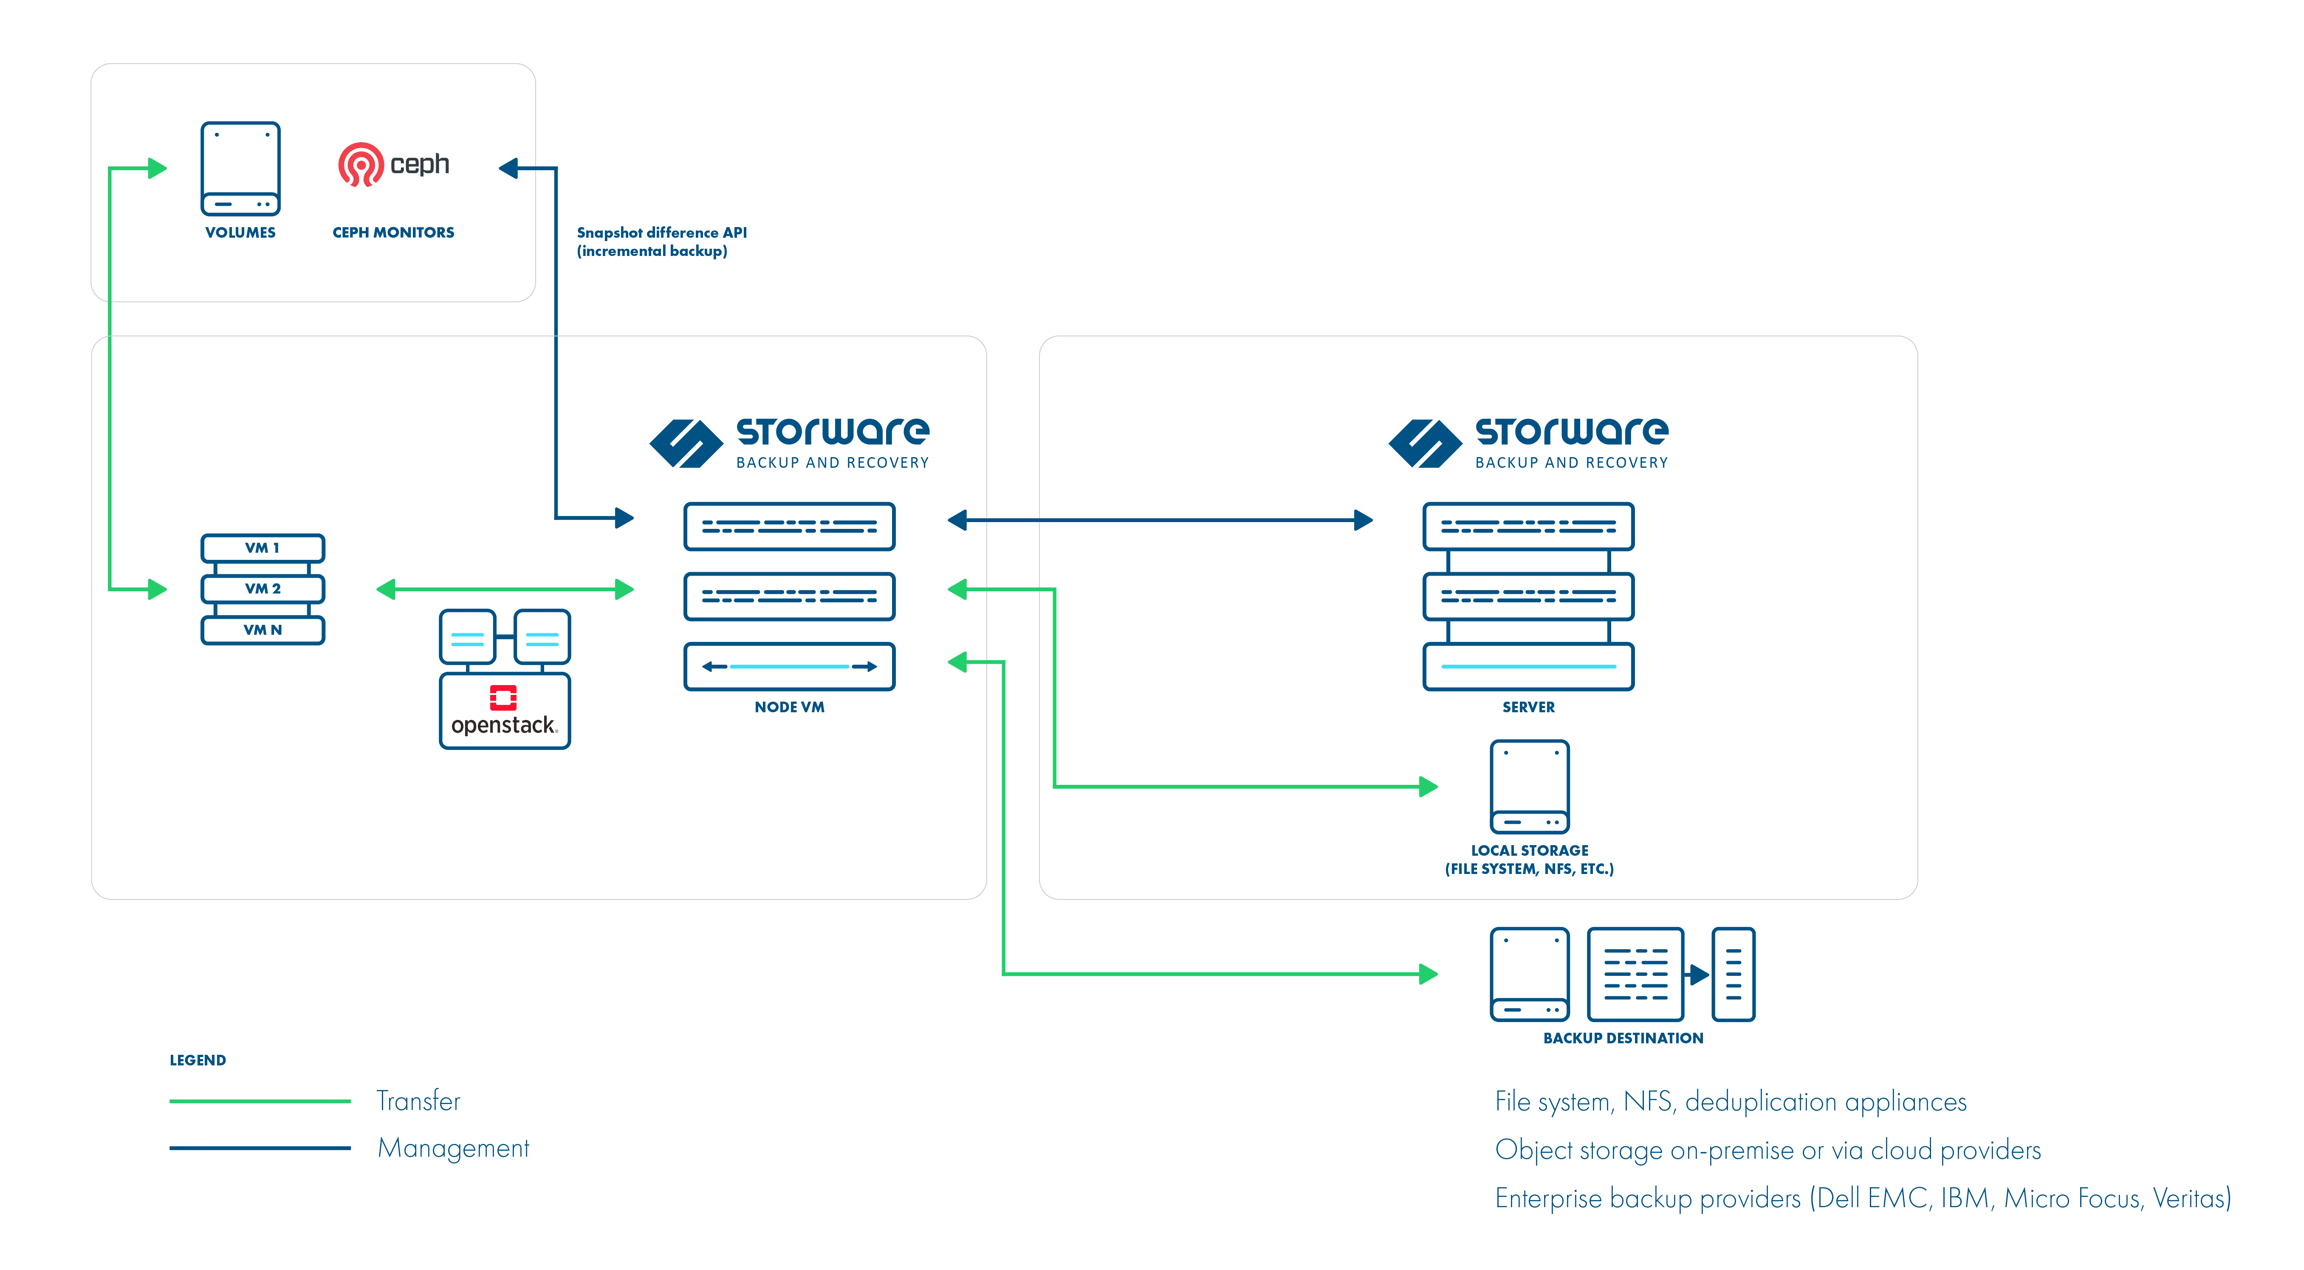
Backup process:
crash-consistent snapshot using cinder API
optional application consistency using pre/post snapshot command execution
metadata exported from API
volumes created from snapshotted disks are mounted one by one to the Proxy VM
data read directly on the Proxy VM
incremental backups supported for Ceph RBD - a list of the changed blocks are fetched from the monitors, and only these blocks are read from the attached disk on the Proxy VM
if an instance is created from the glance image and "download image from glance" option is enabled data is downloaded from glance API, an instance is created from the instance metadata, and the images which are fetched from the glance API
restore creates empty disks on the Proxy VM, imports merged data then recreates the VM using these volumes, it will try to use the image from a glance if present in the target environment or it will upload the image to the glance and register it with the restored VM
Authentication Domains
Storware Backup & Recovery supports OpenStack environments with multiple domains. Each OpenStack Hypervisor Manager needs to have at least one Authentication Domain provided.
Storware Backup & Recovery supports two types of domain authorization:
Unscoped - single credentials to multiple domains
Scoped - credentials to individual domains
Unscoped - single credentials to multiple domains
Use domain-scoped authorization option needs to be turned OFF.
With this setup, the user needs to create only one Authentication Domain. Projects and Virtual Machines are scanned in every domain that the provided user has access to.
Required permissions:
The account must be able to access and enumerate resources in every domain that should be scanned.
Assign to this account an admin role across all domains applicable in your environment, and ensure role inheritance is enabled so access is effective in underlying projects:
You can also use LESS SECURE alternative - system scope:
Scoped - credentials to individual domains
Use domain-scoped authorization option needs to be turned ON.
With this setup, the user can create Authentication Domains for every domain in OpenStack environment. Projects and Virtual Machines are only scanned in the provided Authentication Domains.
Required permissions:
Separate accounts in individual domains must be assigned the admin role on the domain level (not only on a single project).
Inheritance must be enabled so that the domain-level role is propagated “down” to projects contained in that domain.
Tags
Tags in Nova are also scanned (when nova API ≥ 2.26). Tags can later be used in the auto-assignment of the backup policy.
You can list tags for a specific instance in the OpenStack using this command:
Access Keys
During Inventory Synchronization, Storware Backup & Recovery scans all Keypairs (to which a user has access) and lists them as Access Keys. Access keys are not exported during backup. When restoring the instance, in the restore modal -> Advanced tab, the user can specify the Access Key (otherwise, the instance will be restored without one).
Flavors
During Inventory Synchronization, Storware Backup & Recovery scans all Flavors and saves their configuration. When restoring an instance, in the restore modal -> Advanced tab, the user can specify the flavor.
Metadata
This feature introduces support for protecting additional OpenStack metadata during backup and restore operations. Backup jobs now capture extended metadata associated with instances, volumes, and ports. This metadata is stored alongside the backup metadata and can be optionally restored during virtual machine recovery, helping to preserve the original configuration and deployment characteristics of the protected workload.
This feature is fully backward compatible. Existing backups remain fully supported, and restore operations can be performed safely regardless of whether the additional metadata restore option is enabled or disabled.
The following OpenStack metadata is included in backup operations and can be restored during VM recovery.
Instance Metadata
OS-EXT-SRV-ATTR:user_data , config_drive , locked_state , locked_reason, properties, tags, description
Volume Metadata
description, properties, volume_image_metadata
Port Metadata
admin_state_up, description, dns_domain, dns_name, extra_dhcp_opts, numa_affinity_policy, propagate_uplink_status, tags
Restore
Additional metadata restoration can be enabled during virtual machine recovery in the Advanced step of the restore wizard.
The following options are available:
Restore with Instance Metadata – Restores protected instance metadata.
Restore with Disk Metadata – Restores protected Cinder volume metadata.
Restore with Port Metadata – Restores protected network port metadata.
Error Handling
Restoration of additional metadata is performed as a post-import operation. If restoration of any metadata component fails, the virtual machine restore process is not interrupted.
Metadata restoration failures are logged, and the restore workflow continues to completion. This ensures that a successfully restored virtual machine remains available even if one or more metadata objects cannot be applied.
Example log entry:
Administrators should review the application logs after the restore operation to identify and resolve any metadata restoration issues.
Limitations
Storware Backup & Recovery does not backup and restores keypairs that user used in Storware Backup & Recovery doesn't have access to. The restored instance will have no keypairs assigned. In such a case, the keypairs have to be backed up and restored manually under the same name before restoring the instance.
For the libvirt strategy only, QCOW2/RAW files or Ceph RBD are supported as the backend.
The disk attachment method with Ceph requires access to the monitors from the Proxy VM.
Protecting Openstack
Go the Virtual Environments -> Virtualization Providers and click Create
Select OpenStack at the top
In the General tab:
specify Node configuration for the nodes communicating with the keystone
later you can override these settings on the Hypervisor level, but for now, select node config that is able to communicate with your OpenStack KeyStone
if using the disk attachment method, it has nodes residing in their corresponding Proxy VMs
URL - Keystone API URL, e.g.
https://10.201.32.40:5000/v3Region - provide the name of your region (each region must be added as a separate hypervisor manager
Choose import/export mode
Trust certificates - if you're using certificates that may not be trusted by you nodes - e.g. self-signed - you can enable this toggle. By default they will be imported automatically when connecting for the first time anyway.
In the OpenStack settings tab:
Endpoint interface type - interface type used to connect to the OpenStack services' endpoints returned from your Keystone
Download image from glance:
when enabled - this setting only applies when OS (boot) volume is either:
nova volume
cinder volume from image
the image will be downloaded only if the OS (boot) volume is not excluded.
this setting will download the OS image from glance instead of the OS (boot) volume
this means that changes applied to the OS (boot) volume will be discarded, and the original glance image (the one used to create the instance, and in the resulting backup) will be later used for recovery
this may be useful for a disk-attachment strategy (where nova volumes are not supported), and you still need to recover the instance to another OpenStack, where this image doesn't exist.
Use domain-scoped authorization - depending on your use case
single credentials with the permission to access all OpenStack authentication domains and projects -> then this toggle should be disabled, and the credentials should be provided in the only Authentication Domain tab on the left available
separate Authentication domains - then this toggle should be enabled, and all authentication domains used for authentication should be defined on the left with (+) icon
In the Authentication domain tabs (you can use your OpenStack RC file to fill these fields):
Name - name of domain
DomainI ID - optional domain ID
User/Password - OpenStack user and password
Default project - name of default project in the domain being defined
Save and run first inventory sync - this will also detect hypervisors, which may require 2 things:
assigning different node configurations to specific hosts (this must correspond with your AZ setup
providing SSH credentials (when using SSH Transfer backup strategy)
When you want to use the Ceph RBD variant in your backup strategy:
make sure to have this setup done for all nodes that will need access to the Ceph monitors
Make sure that volumes have appeared in Storage -> Instances tab to confirm connectivity between node and Ceph monitors
for each Ceph RBD Storage (volume type), assign your Ceph storage provider and the appropriate Ceph storage pool in Virtual Environments -> Infrastructure -> your hypervisor manager details -> Storage -> volume type -> Ceph settings
When your environment uses an NFS storage backend, make sure to enable QCOW2 file support. Otherwise, backup snapshots will create RAW files (instead of QCOW2):
it's recommended to set these values in
/etc/cinder/cinder.conf:
Run both full and incremental backups to verify the setup.
Instant restore setup
Node configuration
First step to initiate the configuration process for OpenStack Instant Restore service, is creating a directory that will be accessible for mounting by the NFS server. Create a specific directory on your Node machine that will be used as the target space for Instant Restore's shared resources.
Next, create an NFS share that will allow access to the /vprotect_data/ directory from other machines in the network. Sharing this directory will enable OpenStack clients to use it for virtual machine restoration.
Cinder storage backend configuration
After creating the NFS share on the node, you need to configure the NFS backend in the cinder service. This step will allow OpenStack to access resources stored on the node via NFS. Edit the /etc/cinder/cinder.conf file and add this section at the end of the file:
Create the file you provided in the configuration as the value of nfs_shares_config parameter
and path to the NFS share:
After creating the NFS server and configuring cinder, restart the cinder volume service. Please note that the name of this service may be different depending on the OpenStack version.
Matching nodes to the OpenStack storage backends (volume types)
After completing the inventory synchronization of the OpenStack, in Node edition window you can select the storage with the NFS backend configuration. Details about the NFS backend should be supplied by the OpenStack administrator.
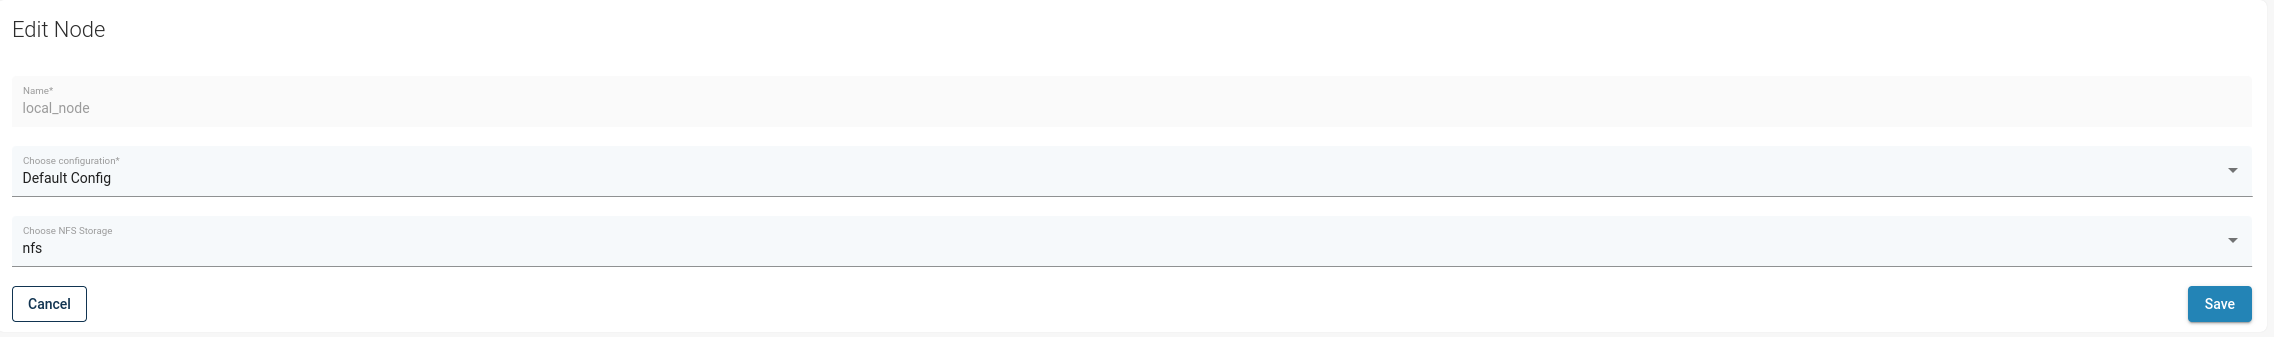
You should now be able to select "Instant restore" for backed up virtual machines.
Limitations
For OpenStack Instant Restore, a dedicated node is required.
Ephemeral disks are not supported.
Last updated